Blog

Welcome to our cybersecurity blog, your trusted source for cutting-edge insights, expert analysis, and practical advice in the ever-evolving world of digital defense, including penetration testing, ethical hacking, and vulnerability assessments. In an era where cyber threats loom larger than ever—from sophisticated ransomware attacks to emerging AI-driven vulnerabilities—we're dedicated to empowering businesses and individuals with the knowledge to stay one step ahead through comprehensive pen testing strategies and robust security measures. Dive into our latest articles on threat intelligence, compliance strategies, innovative security technologies, penetration testing methodologies, ethical hacking techniques, real-world case studies, and vulnerability scanning best practices, all crafted by industry veterans to help you fortify your digital fortress. Stay informed, stay secure!
November 17, 2026

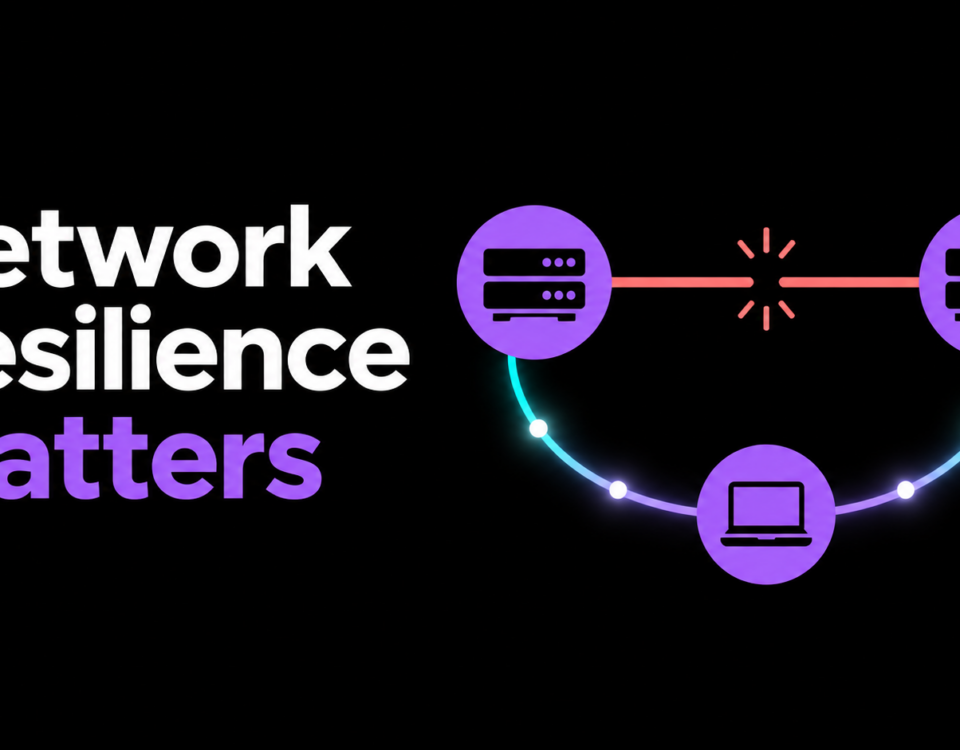
What the NSA Network Outage Reveals About Resilience

Reporting describes an NSA network outage that slowed a classified communications system, with no confirmed cyberattack and a possible link to software upgrades. This brief separates what is reported from what is confirmed and draws the resilience and change management lessons for every organization.
November 17, 2026

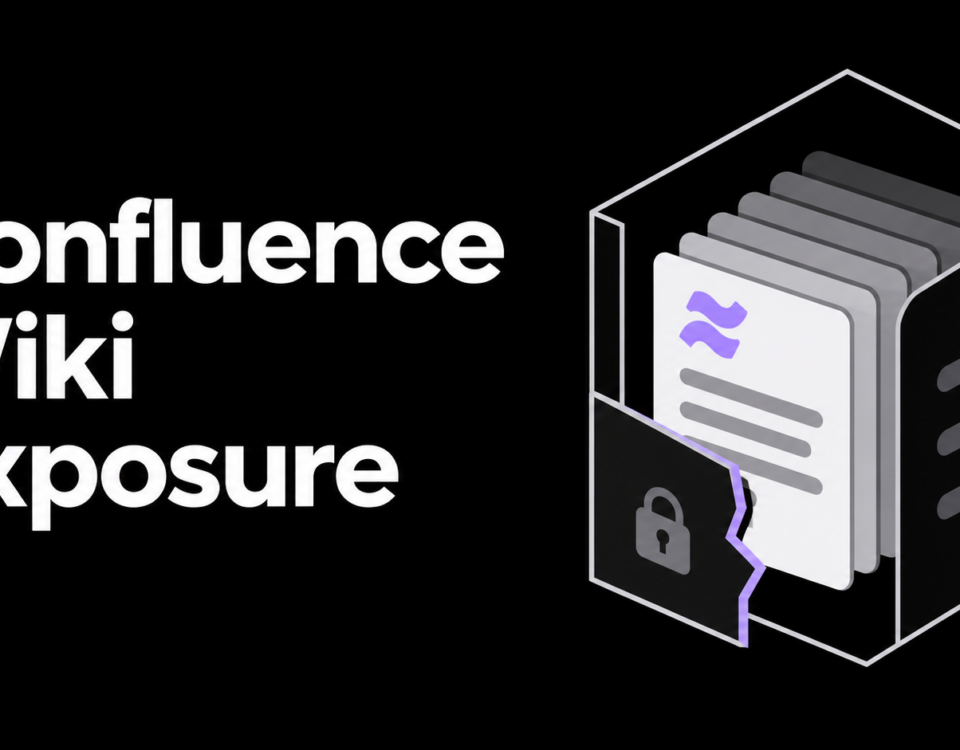
How the Confluence Data Center Flaw Exposes Your Wiki

The Confluence Data Center flaw CVE-2026-90436 gives an unauthenticated attacker remote code execution through the legacy Remote API. This brief covers how the flaw works, which versions are exposed, the 9.2.28 fix, and the one setting that shuts it down.
November 13, 2026

Microsoft 365 Outage: What Happened and the Lessons

The Microsoft 365 outage on November 12 took Outlook and Teams offline for more than 12 hours across 74 countries. This brief covers the timeline, the services hit, why Microsoft says it was not a cyberattack, and the resilience lessons every business should take from it.
November 11, 2026

Urgent: Barracuda Email Security Gateway Root Exploit

An unauthenticated attacker can chain two flaws to root on a Barracuda Email Security Gateway from the admin web interface. This brief covers the exploit chain, the products at risk, the 9.4.0.030 fix, and the checks that confirm whether your appliance already fell.
November 7, 2026

Warning: SonicWall SSL VPN Vulnerability Bypasses MFA

SonicWall patched CVE-2026-19868 on November 6, 2026, and CISA added it to the Known Exploited Vulnerabilities catalog the same day. This guide lists the affected SonicOS versions, the fixes, and the log checks that show whether attackers skipped your VPN login.
October 29, 2026

Warning: PHP2Shell Vulnerability Exploited Before Patch

Amazon recorded PHP2Shell attempts on October 17, four days before PHP shipped fixes, and CISA confirmed exploitation on October 26. This guide covers the timeline, the patched PHP versions, and how to prove that every server you own, including the forgotten ones, is actually closed.
September 23, 2026

Urgent: New AI Malware CLOSEDQUORUM Chooses Its Attacks

Cisco Talos identified CLOSEDQUORUM, a Windows malware sample that polls DeepSeek, Qwen, Mistral, and Gemini to decide whether to steal credentials, inject into a process, or establish persistence no attacker command required. Here is what it does, what defenders should watch for, and what it means for the AI attack classification we track at Digital Warfare.
August 26, 2026

Warning: 5 Proven Enterprise Threat Patterns Exposed for 2026

Enterprise threat patterns in 2026 show attackers moving faster, targeting trusted platforms, exploiting control planes, and turning identity, infrastructure, and automation into high-value attack paths. This article breaks down five proven patterns security leaders must understand now and explains how enterprises can reduce exposure before these tactics become business disruption.

Contact Us Now to Prepare
for Digital Warfare